


Fast learning with high-quality products
There is no denying that preparing for the exam is a time-consuming as well as energy-consuming process without valid SC-500 study guide materials, while the paradox is that a majority of the candidates for the exam are workers who don't have enough time to spend on preparing, and the good news for you is that our company is aimed at solving this problem by releasing high passing-rate SC-500 training materials for all of the workers in this field. We have employed a large number of the leading experts in this field to compile our high-quality SC-500 exam torrent, and we have put forces on the efficiency of our study material. Facts proved that almost all of the candidates can pass the exam as well as getting the certification only after practicing our high-quality SC-500 study guide materials for 20 to 30 hours, which means that you can get success with the minimum of time and effort.
It is easy to understand that the candidates who are preparing for exams (without SC-500 training materials) are very similar to the soldiers who are preparing for the battles, on the one hand, all of them need to spend a lot of time as well as energy and even a large amount of money in the course of preparation (without SC-500 exam torrent), on the other hand, it is inevitable that some people will become winners while others will become losers in the process. Do you want to be the winner (with our SC-500 study guide)? I strongly believe that almost everyone would like to give me the positive answer to this question. Our company is right here to help you to win your personal battle with the minimum of time and effort, because we have spent over ten years in creating the secret weapon for you—our SC-500 training materials. The advantages of our SC-500 exam torrent are as follows.

Favorable price
Our company has a profound understanding of the psychology of consumers and we always would like to take the needs of our customers into consideration (SC-500 study guide materials), it is universally acknowledged that the popularity of a company is driven not only by the vast selection and the high level of customer service, but also -- and mainly -- by the favorable price as well as the deep discounts the company regularly offers. So in order to let our SC-500 training materials available to as many workers in this field as possible, we have always kept the favorable price for our SC-500 exam torrent materials even though our products have been acclaimed as the most effective and useful study materials in this field by all of our customers in the international market.
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Free demo before buying
I dare to say that our SC-500 training materials are the most useful and effective study materials in the field which is 100 percent trustworthy, we are not afraid of any test for our products--SC-500 exam torrent, so we provide the free demo of our SC-500 study guide materials in this website for all of the workers in this field to have a try. We strongly believe that after trying you will be satisfied with our SC-500 training materials and will have more confidence to pass the exam as well as getting the certification, since you will find all of the key points as well as the latest question types are concluded in our SC-500 exam torrent materials. Seeing is believing, if you still have any misgivings just feel free to download our free demo in this website.
Microsoft SC-500 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Manage identity, access, and governance | 20-25% | - Secure access to resources using Microsoft Entra ID - Implement governance with Azure Policy and Defender for Cloud - Secure secrets and keys using Azure Key Vault |
| Topic 2: Secure compute | 20-25% | - Implement security for AI workloads - Implement security for servers and virtual machines (VMs) - Implement security for application platform services |
| Topic 3: Manage and monitor security posture | 20-25% | - Implement Microsoft Security Copilot configuration - Manage security posture using Microsoft Defender for Cloud - Implement activity and event collection in Microsoft Sentinel |
| Topic 4: Secure storage, databases, and networking | 25-30% | - Implement security for databases - Implement security for storage accounts - Implement security for Azure network services |
Microsoft Implementing End-to-End Security Controls for Cloud and AI Workloads Sample Questions:
You have a Microsoft 365 tenant that has Microsoft 365 Copilot enabled for a pilot group.
Users frequently generate responses based on Microsoft Teams chats and Microsoft SharePoint Online sites.
You use Microsoft Purview Data Security Posture Management (DSPM) to identify inversharing risks and create policies based on the recommendations.
You need to manage and edit the policies created by DSPM
Which Microsoft Purview solution should you use?
- A. Data Loss Prevention
- B. Communication Compliance
- C. information Protection
- D. Insider Risk Management
Correct Answer: A 🗳️
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl [email protected]
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 4
You need to ensure that a user named user2-28681041 can manage the properties of the virtual machines in the RG1lod28681041 resource group. The solution must use the principle of least privilege.
Correct Answer:
Check below steps in explanation for Task.
Explanation:
To ensure that a user named user2-28681041 can manage the properties of the virtual machines in the RG1lod28681041 resource group using the principle of least privilege, you can follow these steps:
* In the Azure portal, search for and select the resource group named RG1lod28681041.
* In the left pane, select Access control (IAM).
* Select Add.
* In the Add role assignment pane, enter the following information:
* Role: Select the appropriate role for your scenario. For example, Virtual Machine Contributor.
* Assign access to: Select User, group, or service principal.
* Select: Enter the name of the user you want to assign the role to. For example, user2-28681041.
* Select Save.
https://docs.microsoft.com/en-us/azure/role-based-access-control/role-assignments-portal
You have an Azure subscription that uses Microsoft Defender for Cloud.
You have an Amazon Web Services (AWS) account.
You need to ensure that when you deploy a new AWS Elastic Compute Cloud (EC2) instance, the Microsoft Defender for Servers agent installs automatically.
What should you configure first? sc new
- A. the Azure Connected Machine agent
- B. the classic cloud connector
- C. the Azure Monitor agent
- D. the native cloud connector
Correct Answer: D 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
You have an Azure subscription that contains an Azure SQL database named SQL1.
You plan to deploy an Azure app service web app named Appl.
You need to provide App1 with read and write access to SQL1. The solution must meet the following requirements:
* Provide App1 with access to SQL1 without storing a password.
* Use the principle of least privilege.
* Minimize administrative effort.
Which type of account should App1 use to access SQL1, and which database roles should you assign to App1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:
App1 should use a managed identity . Azure App Service supports system-assigned and user-assigned managed identities that allow applications to obtain Microsoft Entra access tokens without storing passwords, client secrets, or certificates in application configuration. Microsoft specifically recommends managed identities for application access to Azure SQL because they eliminate developer-managed credentials and support passwordless authentication. Microsoft Learn After enabling the identity, create a contained database user in SQL1 that represents App1 ' s managed identity. To satisfy the required permissions while following least privilege, assign that user to db_datareader and db_datawriter . db_datareader permits reading data from user tables and views, while db_datawriter permits adding, modifying, and deleting data. Microsoft documents this role combination for applications requiring normal read/write database access. Microsoft Learn The db_owner role would grant substantially broader permissions, including extensive database administration capabilities, and therefore violates least privilege. A conventional service principal can also authenticate without a user password, but typically requires management of a client secret or certificate unless additional federation is configured. A Microsoft Entra user is inappropriate for an application workload.
You have an Azure subscription.
You configure Microsoft Sentinel to use multiple data sources.
You need to create analytic rules that meet the following requirements:
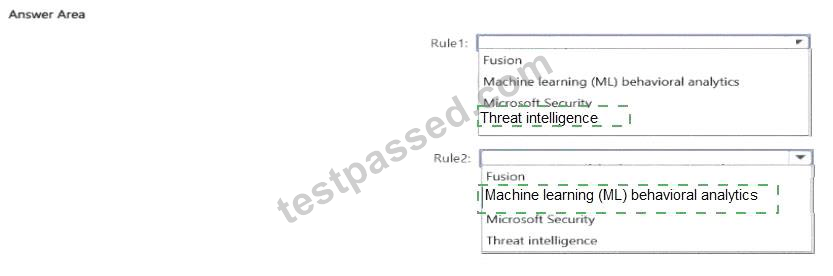
* Rule1: Automatically match Common Event Format (CEF) logs and syslog data with domain, IP address, and URL indicators.
* Rule2: Use Microsoft proprietary algorithms
Which type of detection should you use for each rule? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:
Explanation:
For Rule1 , use Threat intelligence . Microsoft Sentinel provides Microsoft Defender Threat Intelligence matching analytics that automatically correlates threat indicators with supported log data. Microsoft explicitly states that this capability matches CEF logs, Syslog data, DNS events, and other sources against domain, IPv4, and URL threat indicators . For example, entries in the CommonSecurityLog table can be matched against URL, domain, and IPv4 indicators, while Syslog entries can be evaluated against domain and IPv4 threat intelligence. Microsoft Learn For Rule2 , use Machine learning (ML) behavioral analytics . Microsoft describes these rules as using Microsoft ' s proprietary machine-learning algorithms to generate high-fidelity alerts and incidents. They analyze behavioral patterns and detect anomalies that aren ' t easily represented by manually authored static queries. Microsoft Learn Fusion also uses machine learning, but its specific purpose is to correlate multiple lower-fidelity alerts and events into multistage attack incidents. The wording "use Microsoft proprietary algorithms" maps specifically to Microsoft ' s description of ML behavioral analytics .


 Albert

 Kent

 Theresa

 Zebulon
 Broderick
 Page
 Blanche
 Fay
 Nat
 Horace
 Mandy
 Osborn
 Brook
 August
 Blake
 Henry


